
- The issue
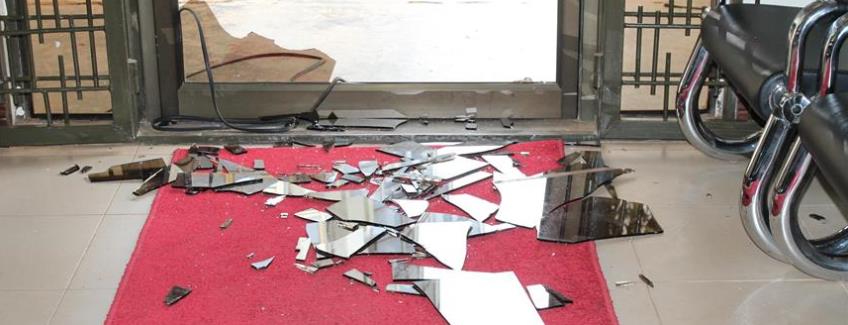
1.1 One of the key risks affecting NGOs and CSOs in Uganda generally is the increasing rate of office break-ins. It just happens when it is least expected. No tip-off. It happened to Action Aid and now to Isis-Women’s International Cross-Cultural Exchange (Isis-WICCE). Like an accident, no one knows the exact date or hour. It just happens. As leaders, can you continue business as usual in such an environment?
- The cause
2.1 The exact cause is not clear. With the words “Isis” in the name, I hope this NGO was not misunderstood. Anyway, jokes aside, your office breach could be due to national security reasons (as was the reported case of Action Aid and GLISS sometime in September 2017) or by petty thieves.
2.2 In the interest of public safety and national security, law enforcement has mandate to break into any office to ‘avert potential security’ threats. However, with the level of access to information governments usually have, it may not be necessary to do an office break-in. After all, with a properly issued court order, Government departments like Police or any person for that matter, can access any office at any time of the day in the presence of the organization leaders or ‘suspects’.
2.3 We also notice that some CSOs and NGOs are in the city outskirts or slums where the general state of physical security is poor. Due to the need to cut costs, some NGOs have moved out of town and turned former homes into offices. This increases the opportunity of petty thieves or disgruntled former employees to plan and execute a ‘tubalemese’ style of break-in. Without conclusive police investigations, we will never know the key threats for effective risk management.
- The solution
3.1 NGOs must speak with one voice to cause government to prioritize CSO/ NGOs office break-in cases and bring the culprits to book. This request is a right and therefore not negotiable. Consistent media campaign in email signatures, website pages, social media and any public square available must be used to bring it to the attention of government to address the issue.
3.2 Develop and implement a practical organisation-wide risk management for the CSO. Email me for a copy of a free enterprise-wide risk management strategy/ framework which is worth US $20,000 but I will share with you free of charge so that you improve your general state of governance and be able to deliver your mandate to support this country. Send email to strategy[at]summitcl[dot]com and or log in and comment on this article. Use the title Request for organisation-wide risk management strategy / framework template.
3.3 Undertake business impact analysis (BIA) and Information Classification exercise. Get a list of all your assets and classify according to criticality to business going concern. Any asset identified as mission critical, make sure that you strengthen its security. For computer resources, set up a disaster recovery site and back up often. In case you lack a budget to invest in a physical backup site, get Amazon cloud hosting and back up your server. For information classified as critical, back it up in a remote location. Whatever you do, invest in disaster recovery and business continuity in practice so that you don’t experience prolonged disruptions following a break-in incident. Remember, whereas you can insure a server or laptop or your computer, your date and software once lost, cannot be recovered. The only solution is to backup at a physically remote site.
For any other areas of good governance, visit our www.summitcl.com/boardtools to change the way you see your organization and transform.
________________________________
In the next Newsletter, Issue 4, I will share about the increasing risk of staff fightbacks. We have noted increasing case of anonymous emails sent to donors and other partners especially after staff terminations. The emails are malicious intended to create confusion and termination of funding by the donors. We explore how you can manage such potential risks before they occur as they pose high reputational strategic risks. You cannot afford to miss the next issue. Know someone who would benefit from these insights? Subscribe them below or forward this newsletter to them. Thanks for sharing.
Success.


0 comments
Leave a comment