
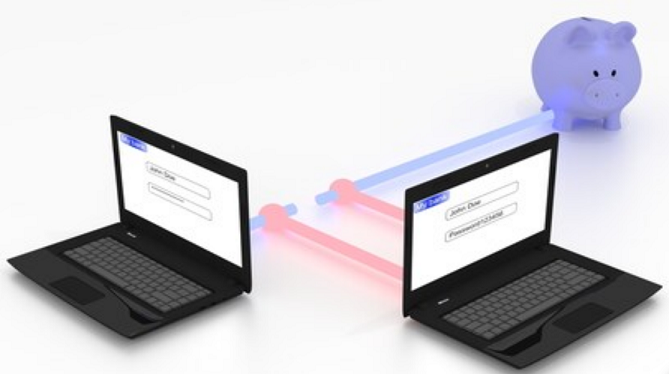
A lay person may not have really acknowledged the risk incurred when communicating over insecure channels but hackers particularly have a way of intercepting and modifying traffic through a Man-In-The-Middle (MITM) attack that is achieved when an attacker poisons the Address Resolution Protocol (ARP) cache of two devices with their respective MAC addresses. Provided the attacker is on the same network as the intended victims, an attack can be initiated from the inside of the network and once the ARP cache has been successfully poisoned, each of the victim devices send all their packets to the attacker when communicating to the other device, and the attacker can easily monitor all their communication.
Just to prove this threat, we can run an actual ARP poisoning attack, redirecting the flow of packets and making it flow through a user PC running Windows 7. We shall specifically use a tool called arpspoof which we can use to launch the MITM attack in Kali Linux.
When connected now to the target network, we are going to basically tell the Client that we are the Wi-Fi router, and shall similarly fool the router that we are the Client, and in that way we shall be in the middle of the packet flow, between the Client (10.0.2.5) and the Wi-Fi router (10.0.2.1), and all the packets will start flowing through our device. We shall first of all find the MAC addresses of the victim (Windows 7) and attacker (Kali Linux). We can see we have the gateway at 10.0.2.1, and the MAC address 52-54-00-12-35-00 in the figure below.

After the attack we check the Windows ARP table and find that it has been successfully poisoned, and the MAC address is changed.
So, what’s the way forward?
- Set up static ARP entries in the ARP cache for any two hosts that communicate regularly with each other. Static IP address-to-MAC address mappings in the local ARP cache will prevent spoofing to a considerable degree.
- Use ARP spoofing detection tools that can block illegitimate ARP packets. AntiARP, for instance provides Windows-based spoofing prevention at the kernel level, and ArpStar which is a Linux module for kernel 2.6 and Linksys routers, drops invalid packets that violate mapping and contains an option to heal. Similarly, Dynamic ARP Inspection (DAI) in Cisco Catalyst 6500 Series Switches discards ARP packets with invalid IP addresses, such as 0.0.0.0 or 255.255.255.255, and ARP packets containing MAC addresses in their payloads that do not match the addresses specified the Ethernet headers.
- A Virtual Private Network (VPN) will secure your online activities through an encrypted tunnel.
It has been noticed over time that people are the weakest link in enforcing security and in that regard, Summit Consulting Ltd brings you a Cyber Security Awareness Training course at your premises to bring forth awareness on the various forms of cybercrime and attack schemes that could be executed on your network, alongside the defensive measures.
Join Summit Consulting Ltd in partnership with IFIS on our annual cyber-security awareness and risk management conference, which is scheduled to take place from the 16th, 18th October 2019. You need to get sensitized about all forms of fraudulent practices that can render your company insecure, followed by recommended remedies against those practices.


0 comments
Leave a comment