
You have a penetration testing process.
You have a risk management department.
You have an internal audit team.
Yet you are still vulnerable. Why?
Because most teams are not evolving as fast as the threat landscape.
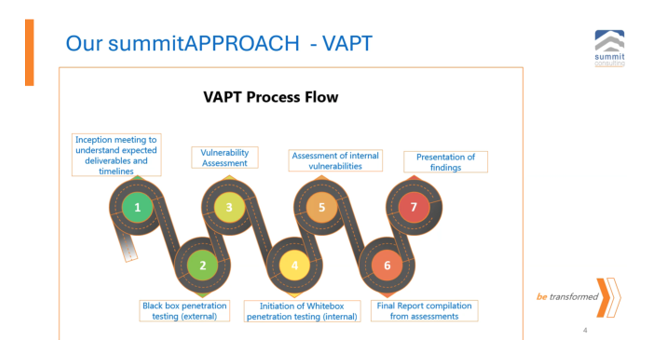
At Summit Consulting, our VAPT approach is simple and brutal:
- Inception meeting: Define timelines, expectations, and failure points up front.
- Blackbox penetration testing: Simulate a real-world external attack without insider knowledge.
- Vulnerability assessment: Identify cracks before the enemy does.
- Whitebox penetration testing: Simulate insider threats with full access.
- Internal vulnerabilities assessment: Your weakest links are always inside.
- Final report compilation: No sugar-coating. Just the truth.
- Presentation of findings: Executive-level intelligence, not geek talk.
Here’s the real question
Are your internal audit and risk teams evolving to meet today’s threats?
Or are they still stuck writing yesterday’s audit checklists?
Cyber risk is not a compliance exercise anymore.
It is a survival strategy.
Why most risk management teams are not future-ready
In 2024, a mid-sized Ugandan financial institution asked us for a routine vulnerability assessment. They had just passed a regulatory audit with flying colours. Their internal audit team had ticked all the boxes.
We applied our summit iShield 7-step VAPT approach.
- Inception meeting: Their IT head assured us, “We’re clean. Just do a quick scan.”
- Blackbox testing: Within 4 hours, we breached their email gateway and sat silently inside their network.
- Vulnerability assessment: Found 47 high-risk exposures, including default admin credentials on core switches.
- Whitebox testing: Gained domain admin privileges in less than a day, with full access to their backup systems.
- Internal vulnerability check: Discovered weak passwords like “Welcome@123” and unpatched ERP servers.
- Final report: We drafted a 54-page red alert report with proof-of-exploit screenshots.
- Board presentation: Their CEO nearly fell out of his chair. His exact words were: “But our IT team said we were safe?”
Here’s the reality
Their internal audit team had never tested controls, only reviewed paperwork.
Their risk team didn’t even understand what a lateral movement attack was.
That is the problem.
Too many organizations are blind, not because they lack talent,
But they confuse compliance with security.
They are auditing locks, not testing doors.
Our VAPT approach is not just a scan, it’s a war game.
If your internal experts can’t handle simulated attacks, how will they survive real ones? Now is the time to partner with experts who can support them to add value. Future-ready internal audit and risk management team, outsource the cybersecurity assurance services to an external firm so that they do not move blindly.
Leadership takeaway
Compliance passed.
Pen test failed.
Only one of those outcomes protects your business.
Wake up. Test. Transform. Contact us today to be your partner. Visit www.summitcl.com.
#RiskManagement #InternalAudit #CyberSecurity #VAPT #BeTransformed #MrStrategy



0 comments
Leave a comment